Repository navigation


|
Hello there, I have just set up argo workflows with sso access. Configured a read-only service account and bound it to it a role that is supposed to grant only read permissions for everything related to argo workflows, this SA seems to be assigned to users when they log in to argo workflows but they are still able to create workflows and others resources using the GUI. I am not able to see what did I do wrong, any help would be appreciated.
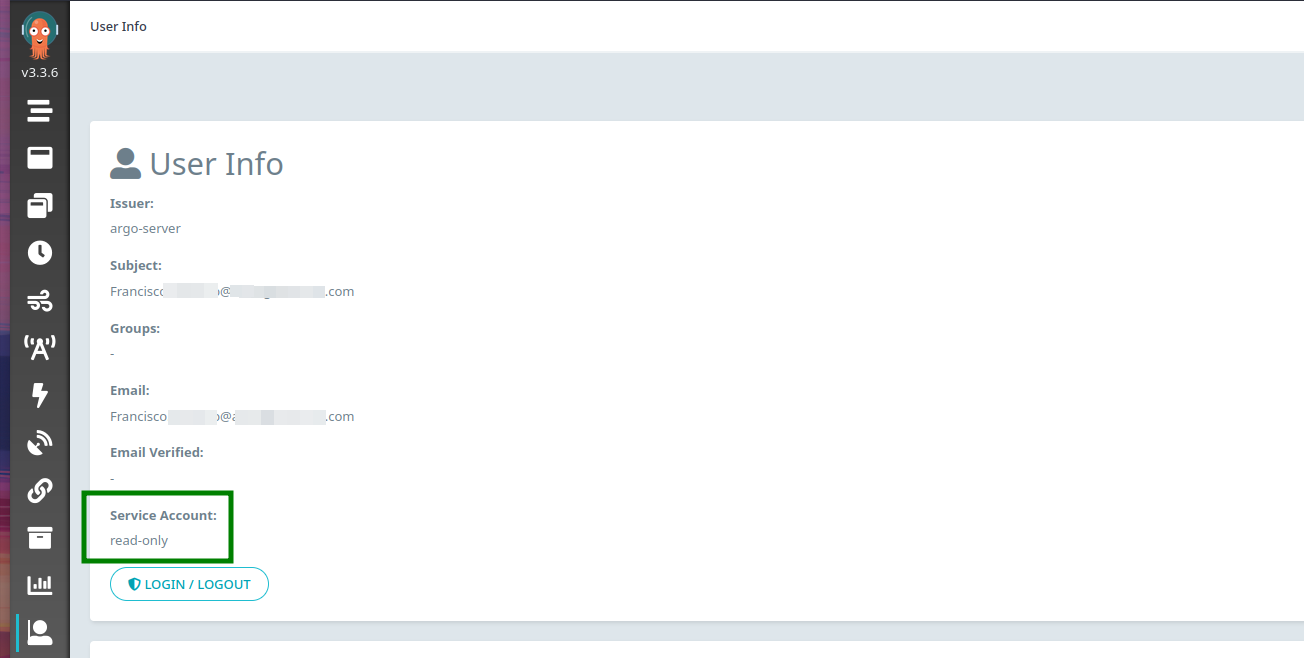
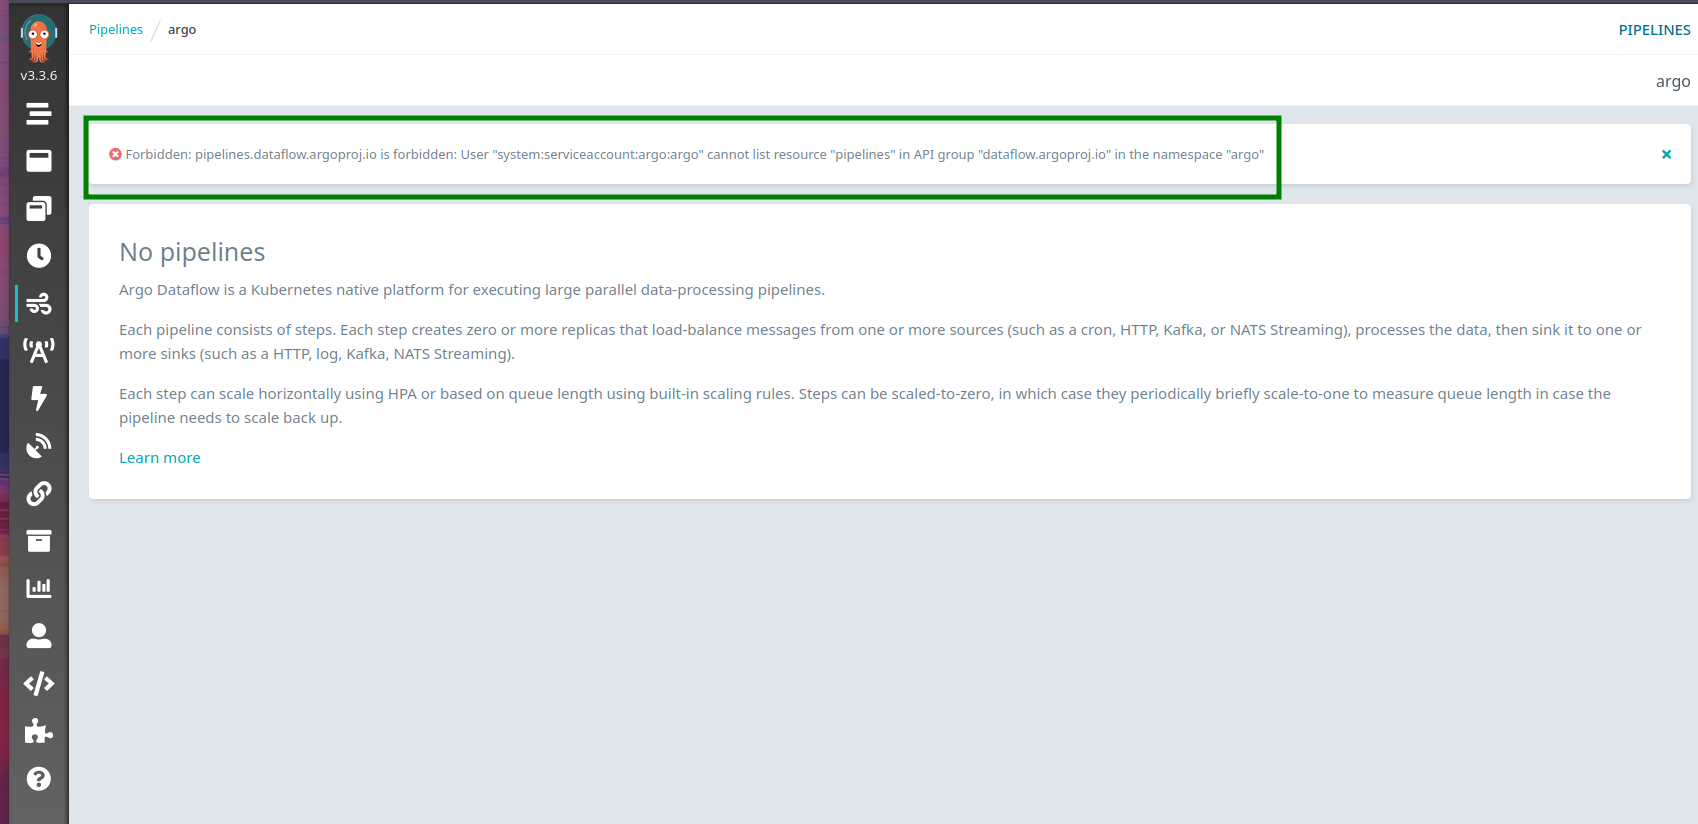
This is the role that I created: The sa: And the role binding: An interesting issue that I have found is that, if (after logged and with this read-only service account assigned) I go to the Pipelines view in the GUI I see this error message:
This doesn't make too much sense to me because it should be applying the serviceaccount:read-only as shown in the other screenshot, on the user login page. Any ideas? thanks for your help in advice! |
Replies: 4 comments 1 reply
|
Also: |
|
Ok so I made some changes to the argo-cluster clusterrole because it seemed like despite being logged and having a different SA assigned, I was getting the permissions of the argo service account. So I edited the cluster role of this service account and now, when I try to create a new workflow I get: |

|
Are you enable rbac on sso workflow-controller-configmap? The pipeline error permissions are normal, because for use that object kind you need argo dataflow installed. I have the same workflows versión integrated with Keycloak like SSO and I haven't got that problem. |

|
Ey Diego, thanks for your answer, yes, I enabled RBAC on workflow-controller-configmap sso, and actually, the error that I mentioned above doesn't happen with a clean installation. My problem is that anyone connected through sso CAN create workflows without any issue and I don't want that. So I created a read-only service account and make it the default one.... without permission to create workflows, but the users still can create them. Then I tried removing permissions from the default account and now the users cannot create workflows, they receive the error above which indicated to me that somehow argo is applying the wrong SA to the users although in the user info page it shows the read-only account. I wonder if this could be a bug or I may be doing something wrong. |
|
Ok so... I think my problem was that I had defined the read-only account with a namespaced role while argo workflows server and workflow controller pods were configured in the whole cluster... so I was able to create workflows in the default namespace. I added the --namespaced flag to the two pods and make sure that the read-only account doesn't have permissions to create workflows there and now everything works as expected. |


Ok so... I think my problem was that I had defined the read-only account with a namespaced role while argo workflows server and workflow controller pods were configured in the whole cluster... so I was able to create workflows in the default namespace. I added the --namespaced flag to the two pods and make sure that the read-only account doesn't have permissions to create workflows there and now everything works as expected.